

On March 18, Splunk's annual event 'Splunk Go 2026 Seoul' was held at The Westin Josun Seoul Parnas Hotel in Gangnam-gu, Seoul.
CloudNetworks, a Splunk partner company, participated as an official sponsor at this event following 2024, operating a booth in the exhibition zone. We've captured the on-site story of a day spent amid the heated enthusiasm as many people flocked in even before the event began.
📸CloudNetworks, Splunk Go Seoul 2026 Event Sketch
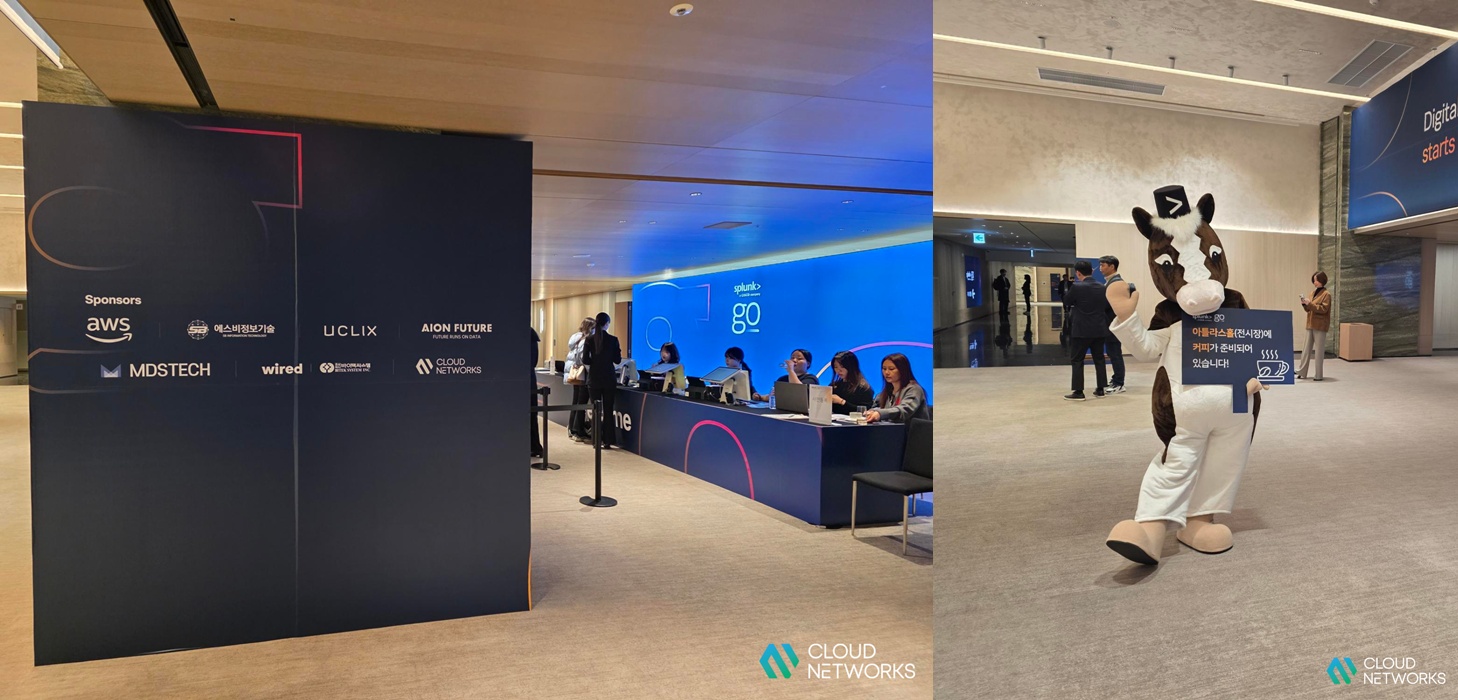
At the entrance to the venue, Splunk's mascot Buttercup warmly greeted attendees. When we took a photo, it struck a great pose.
🤖The New Standard of Digital Resilience Completed with AI, Splunk
In the AI era, the real challenge companies face is not adopting AI, but how quickly and stably they can operate their AI environment. This event's theme was 'Digital Resilience Completed with AI,' and 'Agentic Speed,' put forward by Splunk, was the answer.
In his keynote, Splunk Global CTO Cory Minton emphasized that the capability to interpret and act on the explosively growing machine data—alongside the spread of AI—more quickly is what divides corporate competitiveness. In the security domain, the 'Agentic SOC' strategy, which unifies SIEM, SOAR, and UEBA into one to automate everything from detection to response, and in the IT operations domain, the 'Agentic Observability' strategy, which provides integrated observation of AI systems' performance, cost, and security, were introduced together with concrete roadmaps. Machine Data Lake, slated for release in the first half of the year, and AI Agent Monitoring, which has already transitioned to general availability, allowed attendees to see at a glance the direction in which the Splunk platform is evolving to fit the AI era.
Customer case studies also added to the on-site energy. Real experiences from various industries—including security, manufacturing, and retail—were shared, from NH Nonghyup Bank's AI-based security monitoring automation, to LG Electronics' case of combining its physical AI solution 'EVA' with Splunk to secure operational stability for large-scale AI service operations, to E-Mart's AppDynamics implementation case. In the afternoon, the talk-show-style session "Can Splunk Interpret AI Too?", in which Splunk engineers unpacked how Splunk AI capabilities such as AI Toolkit, RAG, and MCP are used, drew high interest from attendees.
👥The Splunk Go 2026 Exhibition Zone, Joined by Partners
A different atmosphere unfolded in the exhibition zone. Not only Splunk but also numerous partner companies operated their own booths there, keeping a lively mood going throughout the event. Attendees freely chatted over catering and in lounge spaces set up throughout the area, with exchanges continuing even between sessions.
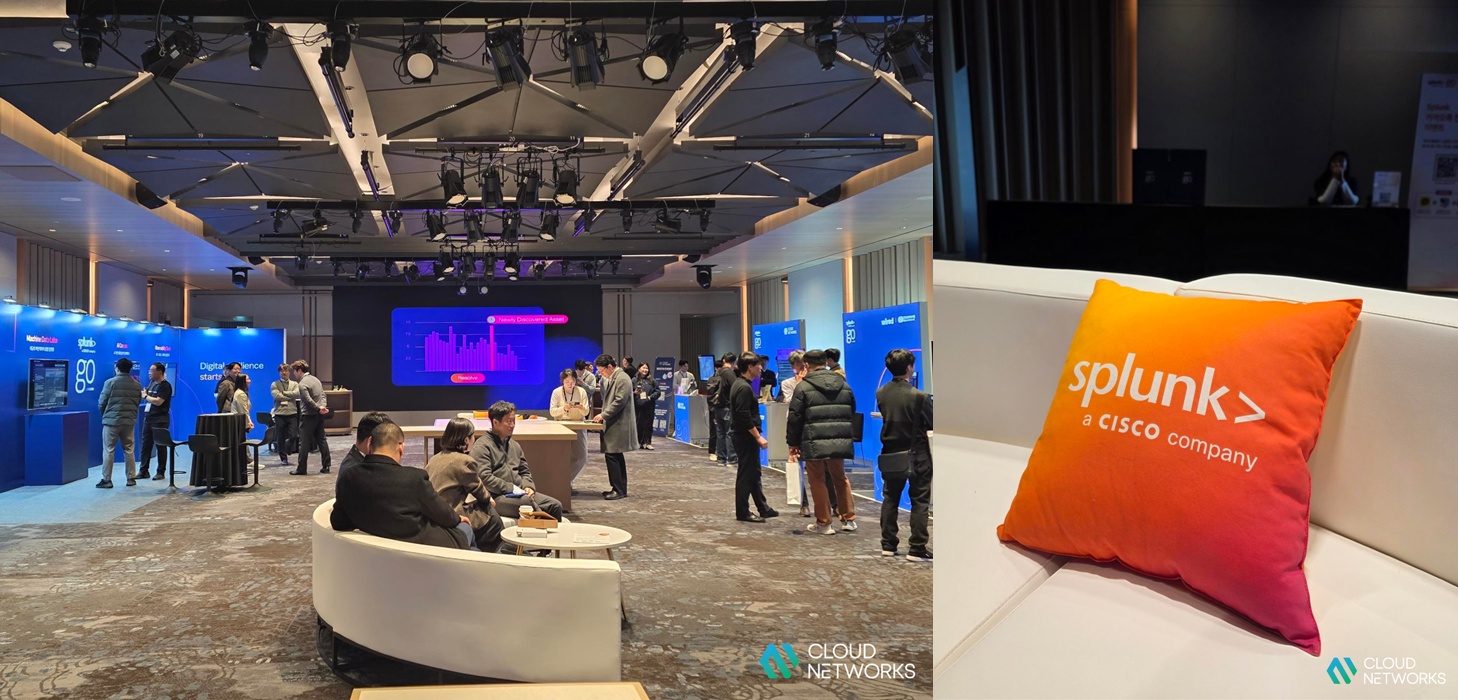
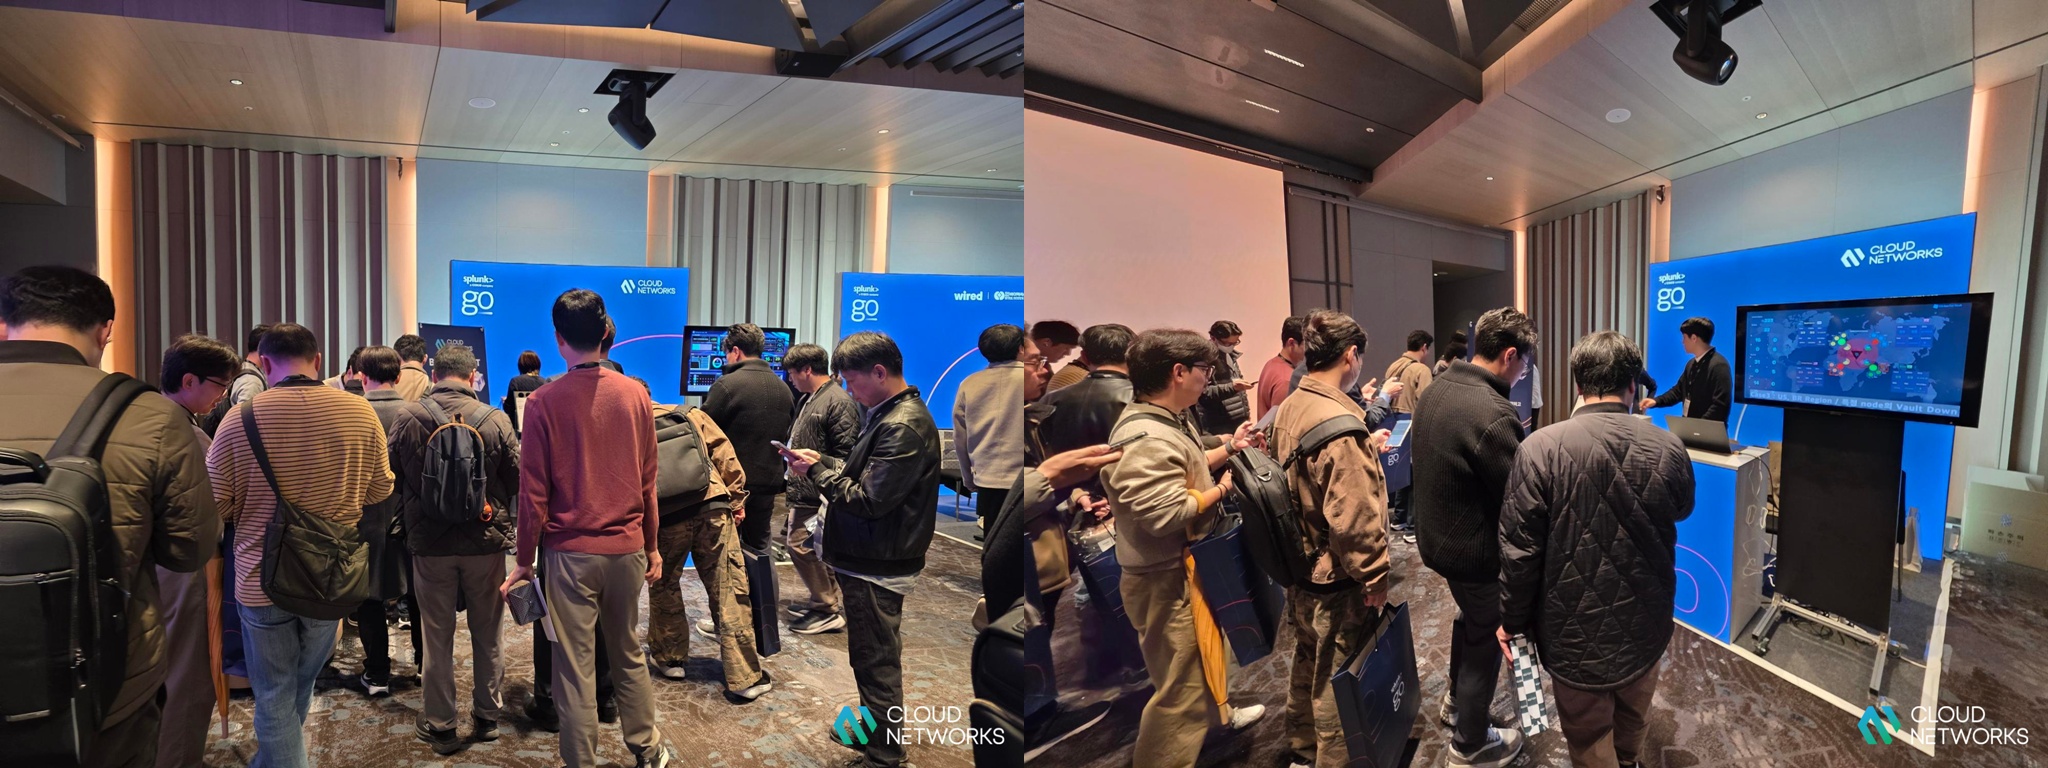
CloudNetworks also set up a booth in one corner of the exhibition zone to welcome attendees. Following 'Splunk .conf Go Seoul' in 2024, this was another occasion to present directly at a Splunk event site. At the booth, demonstrations of CN-Eye for Vault ran continuously, and a solution portfolio brochure offering an at-a-glance look at CloudNetworks' solutions and services was also prepared for interested visitors to take freely.
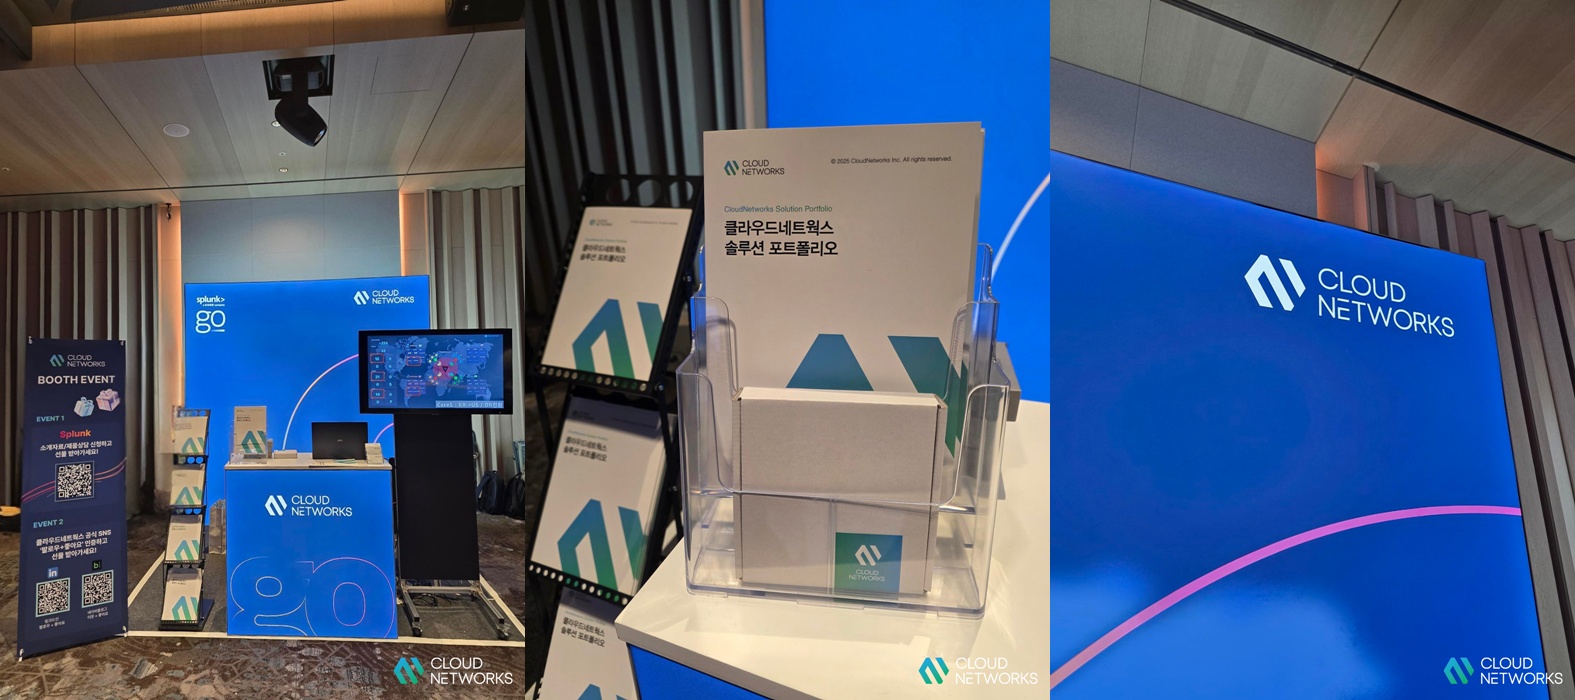
What was put front and center at this booth was 'CN-Eye for Vault,' a cloud security automation monitoring solution developed in-house by CloudNetworks based on Splunk. CN-Eye for Vault integrates and visualizes, within a single Splunk dashboard, the key information needed for operations—from the status of HashiCorp Vault's secrets management, to cluster status, to DR failover monitoring. The on-site demonstrations and explanations were handled directly by the Big Data Convergence Team, who bring extensive experience in building and operating Splunk, and they also communicated naturally in English with foreign attendees while continuing the demonstrations.
Quite a few people requested detailed explanations of CN-Eye or kept asking follow-up questions, and there were also questions touching on this event's key themes, such as AI utilization approaches, Agentic Security, and Agentic SOC. There were no small number of inquiries about specific products such as Splunk SIEM and SOAR as well.
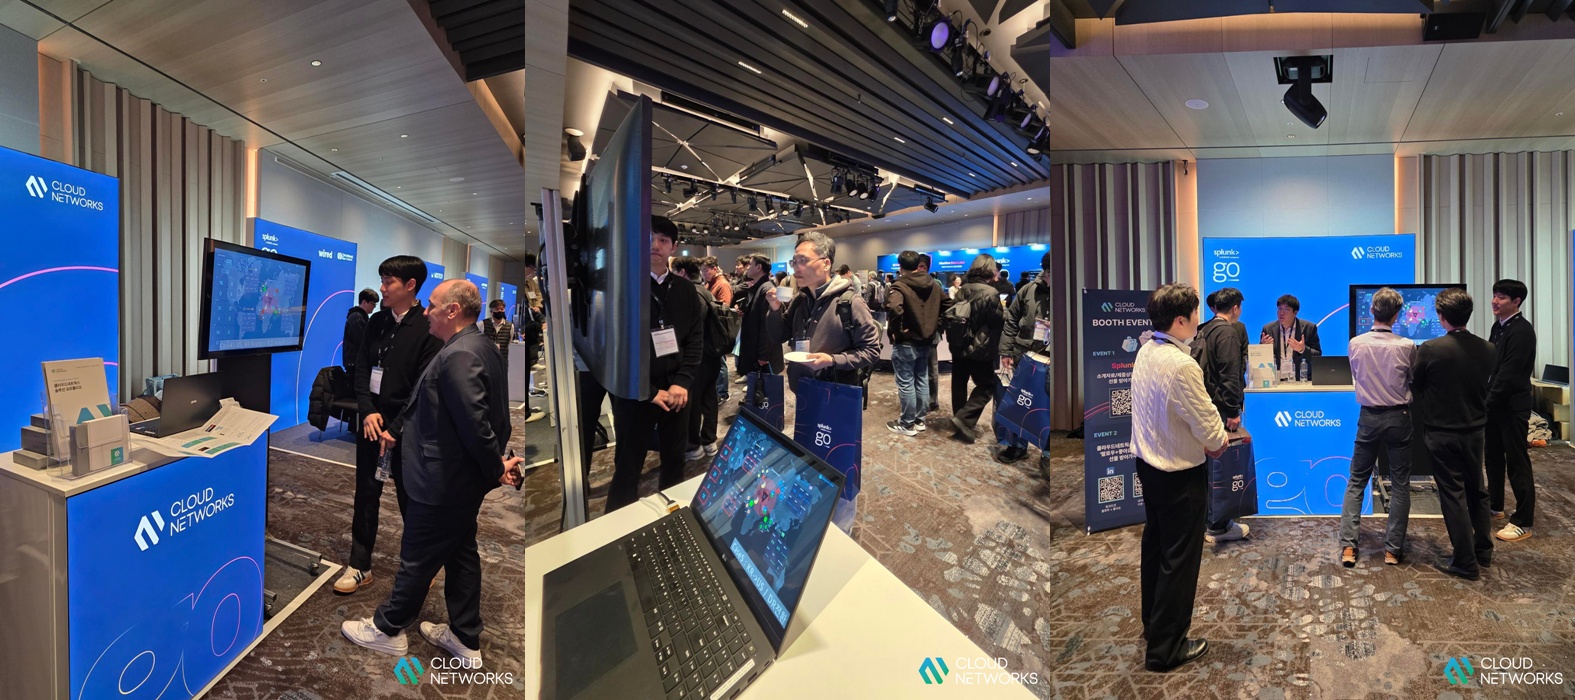
Two booth events were also held on-site: an event offering a gift to those who requested Splunk introductory materials or product consultations, and an SNS event offering a gift to those who followed CloudNetworks' official LinkedIn and Naver Blog and verified with a "like." Thanks to more people than expected actively participating, the response was so enthusiastic that all the prepared gifts were used up.
This Splunk Go 2026 Seoul was a meaningful occasion where CloudNetworks, as a Splunk partner company, was able to directly showcase its technology and solutions to many attendees. We sincerely thank everyone who visited our booth and showed interest.💛
CloudNetworks is a partner company that has worked together with a wide range of client companies, including large-scale enterprise environments, on Splunk implementation, operation, and support. From developing custom dashboards tailored to customer needs to developing in-house solutions such as CN-Eye for Vault, CloudNetworks works together with its clients based on a deep understanding of the Splunk platform and strong technical capabilities. If you're curious about adopting Splunk or about CloudNetworks' solutions, please check the link below for more details or feel free to reach out anytime.
▶ Learn more about Splunk