

SIEM has long been understood as a tool for collecting logs and generating compliance reports. Today's SIEM has expanded into a domain that includes real-time detection, alert correlation, behavioral analytics, threat investigation, case management, and automated response. Capabilities that were once separate product categories—UEBA and SOAR—are now expected as standard elements within SIEM.
As the role has broadened, so have the selection criteria. It is no longer enough to look only at detection engine performance. Organizations must also examine what kind of working environment the platform provides for analysts who spend their entire day in it, whether security data and IT operations data can be handled without duplication, and whether detection content tailored to the organization's own environment can be built and improved in-house.
The "IDC MarketScape: Worldwide SIEM 2026 Vendor Assessment," published in June 2026, organizes these considerations into evaluation criteria. This article reviews the SIEM evaluation criteria presented in the report, then summarizes the assessment of Splunk—named a Leader under those criteria—along with the key capabilities of Splunk Enterprise Security.
☑️ The IDC MarketScape 2026 SIEM Assessment
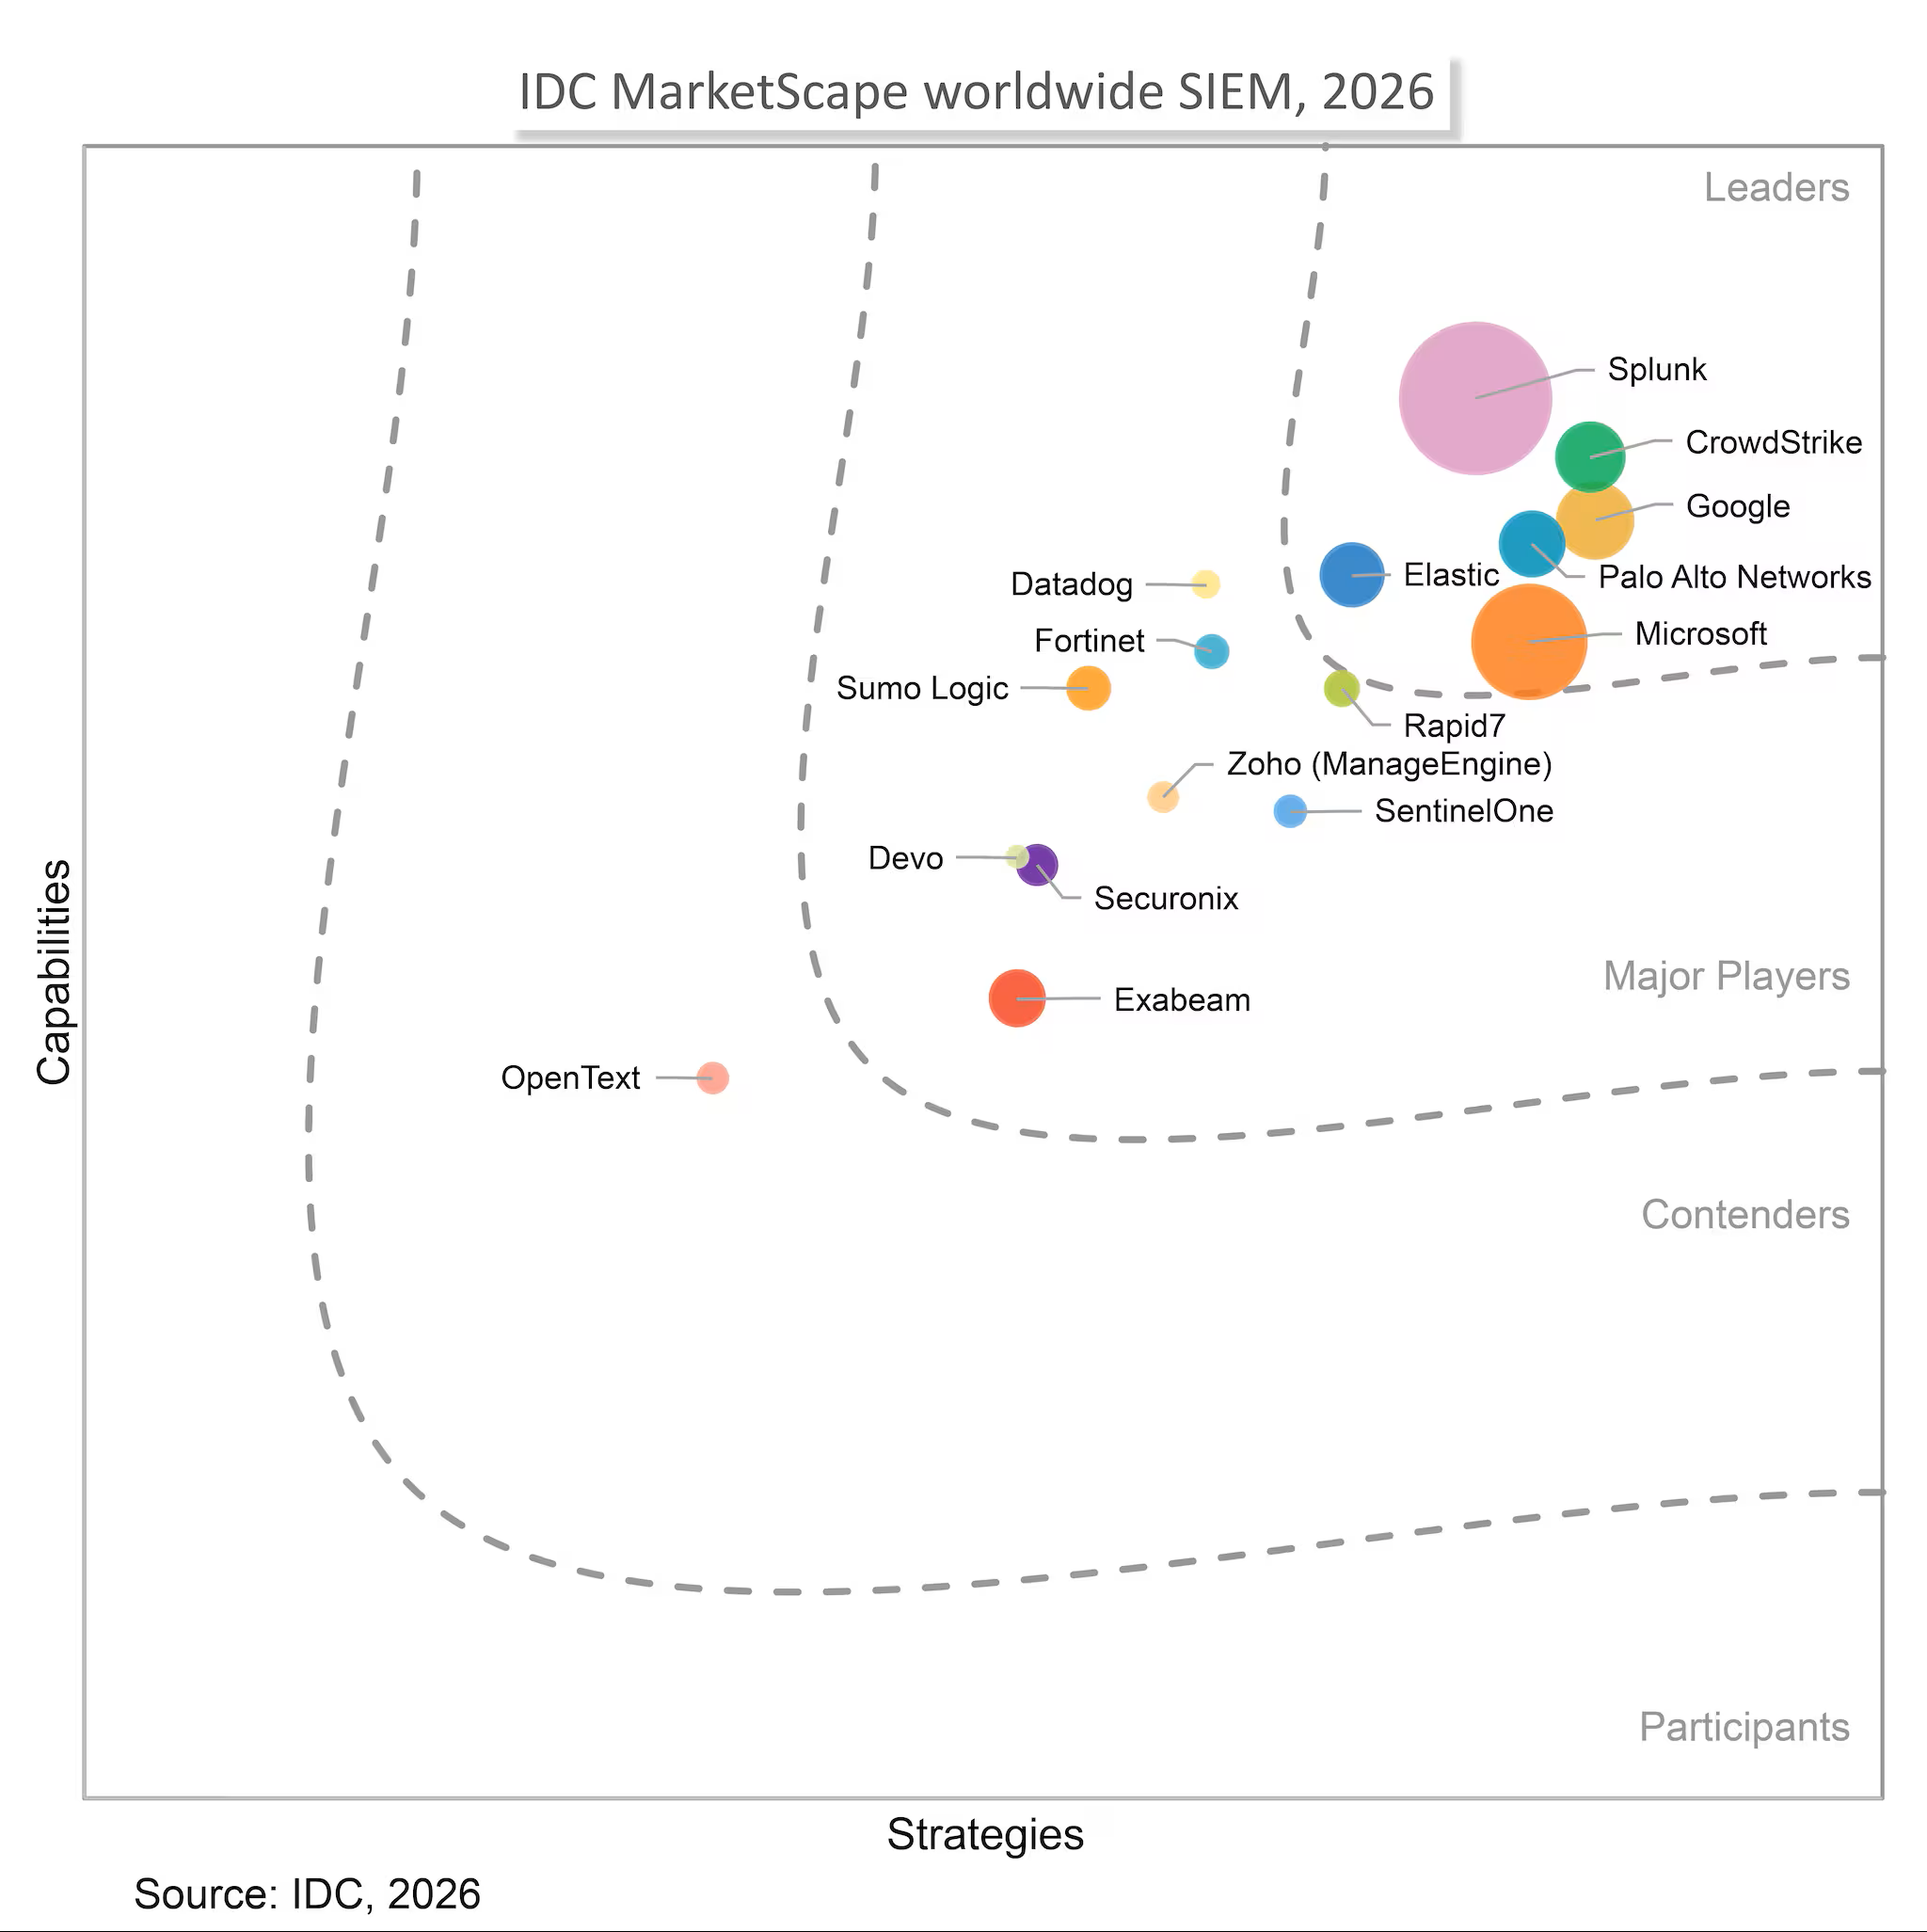
This assessment measures SIEM vendors' current capabilities together with their medium-term strategy to map out their position in the market. The following sections cover the results and the assessment methodology in turn.
☑️ Splunk's Assessment Results
Splunk was positioned in the Leaders category in this assessment, following its placement there in the 2022 and 2024 assessments as well. Four strengths were cited: an integrated investigation structure that combines SIEM, SOAR, UEBA, and Attack Analyzer in a single workspace; a broad base of community-accumulated detection content; an architecture that processes security and operational telemetry on the same data plane; and deployment flexibility that lets customers choose where their data resides without changing the analyst experience.
☑️ IDC MarketScape's Assessment Methodology and Inclusion Criteria
IDC MarketScape is an analytical model that applies both qualitative and quantitative scoring to represent each vendor's position within a single graphic. Vendor scores are derived from detailed vendor surveys and interviews, publicly available information, and actual customer experience.
The assessment uses two axes. The y-axis reflects how well a vendor's current capabilities and service offerings align with customer needs today. The x-axis represents how well the vendor's future strategy aligns with what customers will require over the next three to five years. In the graphic, the size of each vendor's marker represents that vendor's market share within the relevant market segment.
The criteria for inclusion in the assessment are also specified:
- The product must be marketed as a SIEM, not as XDR, NDR, security analytics, or log management.
- It must be commercially available in a form the customer manages directly, rather than as a vendor-managed offering.
- It must collect telemetry from multiple security sources rather than being limited to a single cloud or security platform.
- It must be a globally available product sold in at least four global regions.
- It must have achieved at least $50 million in SIEM revenue as of 2025.
This is what makes a Leader position meaningful: the result is not determined by current product functionality alone, but by an evaluation of current capability together with three-to-five-year strategic alignment, conducted among a vendor group that already meets global sales scale and revenue requirements.
☑️ What Practitioners Value Most in SIEM Evaluations
In IDC's survey of security practitioners, two factors consistently ranked at the top as important elements of SIEM: the real-time detection engine and the analyst's investigation experience.
Operational complaints cluster around the same points. The two biggest operational pain points organizations cite are detection tuning and investigation workflow. Detection rules that fire too broadly require ongoing calibration to reflect the context of the organization's environment. Investigations that require analysts to move between multiple tools delay response and increase analyst cognitive load. According to IDC, a SIEM that provides asset context and threat intelligence directly within the investigation interface directly reduces this friction.
The scope of data collection is also flagged as an issue. According to IDC's survey, 73% of organizations collect less than 75% of the data needed to fully monitor their environment. The cause of this gap is attributed not to technology but to cost and complexity. Volume-based pricing models create tension between log collection scope and budget, and organizations resolve this tension by excluding data. The blind spots created this way become the points where attackers operate.
In summary, today's SIEM evaluation comes down to four questions: Can investigations be completed within a single screen? Can detections be built to fit the organization's own environment? Can data that was excluded for cost reasons be brought back into collection scope? Can the organization choose where its data resides to meet regulatory requirements? The strengths cited for Splunk connect directly to these four questions.
☑️ Splunk's Strengths as Assessed by IDC MarketScape
1. Unified Investigation Completed Within a Single Workspace
The first strength is that Splunk Enterprise Security Premier combines SIEM, SOAR, UEBA, and Attack Analyzer within a single workspace. Shared case management and finding-based detection are applied on top of this, grouping correlated events into a single investigation view. This directly addresses the investigation workflow problem mentioned earlier—the delay and cognitive load that result from analysts moving between multiple tools. In environments with limited analyst headcount, the time spent per investigation directly determines how many cases can be handled, so a structure that reduces screen-switching is directly tied to operational scale.
2. A Broad Base of Community-Accumulated Detection Content
The second strength is community. Customers regard Splunk's community—including the .conf conference, user groups, and Splunkbase—as a meaningful resource for peer learning and content sharing. The assessment notes that user-developed content accumulated on Splunkbase and in community forums helps organizations build detections suited to their own environments. Detection content is an area that must continue to expand even after SIEM deployment; vendor-provided default detections alone are rarely sufficient to meet every industry- and environment-specific requirement. A broad base of reference content that can be adapted directly affects both the initial burden of onboarding and the pace at which operational maturity is reached afterward—an asset that doesn't show up in a feature list but only forms over a long-accumulated user base.
3. A Data Architecture That Processes Security and Operational Data on a Single Data Plane
The third strength is data architecture. The Splunk platform collects security telemetry and operational telemetry on the same data plane. This structure was cited as supporting both security and IT teams while minimizing duplicate data ingestion—made possible because Splunk shares the same data analytics engine across SIEM as well as observability and IT operations use cases. Read against the 73% data collection gap mentioned earlier, the significance becomes clear: in a SIEM environment where collection volume directly drives cost, reducing duplicate collection means monitoring a wider scope within the same budget. Organizations already collecting logs for IT operations monitoring purposes should factor in the cost and management overhead of building a separate pipeline for security purposes.
4. Deployment Flexibility to Choose Where Data Resides
The fourth strength is flexibility in deployment and data location. Splunk Enterprise Security can run as a self-managed deployment based on Splunk Enterprise, or as SaaS based on Splunk Cloud Platform hosted on AWS, Azure, or Google Cloud Platform. This is combined with separation of compute and storage, SPL2 pipelines via Edge Processor and Ingest Processor, and federated search targeting Amazon S3 and Amazon Security Lake. The essence of the assessment is that customers can choose where their data resides without changing the analyst experience. In domestic financial, public-sector, and manufacturing environments subject to data residency requirements or network segregation policies, this item has a direct impact on architecture design. Whether it makes more sense to centralize all data in one place or to leave it in place and connect to it via search depends on regulatory requirements and data volume.
☑️ Environments Where Splunk Enterprise Security Is a Good Fit
IDC MarketScape also presents the conditions under which Splunk Enterprise Security is worth evaluating.
First, large enterprises in hybrid or multi-cloud environments that need federated search across on-premises and cloud data stores, and that want to collect security and operational telemetry on a single platform.
Second, SOC teams that don't want to rely solely on out-of-the-box content, but instead want to write, tune, and iteratively improve their own detections and analytics using a powerful, flexible query language. Such teams were assessed as having a particularly high fit.
☑️ Key Capabilities of Splunk Enterprise Security
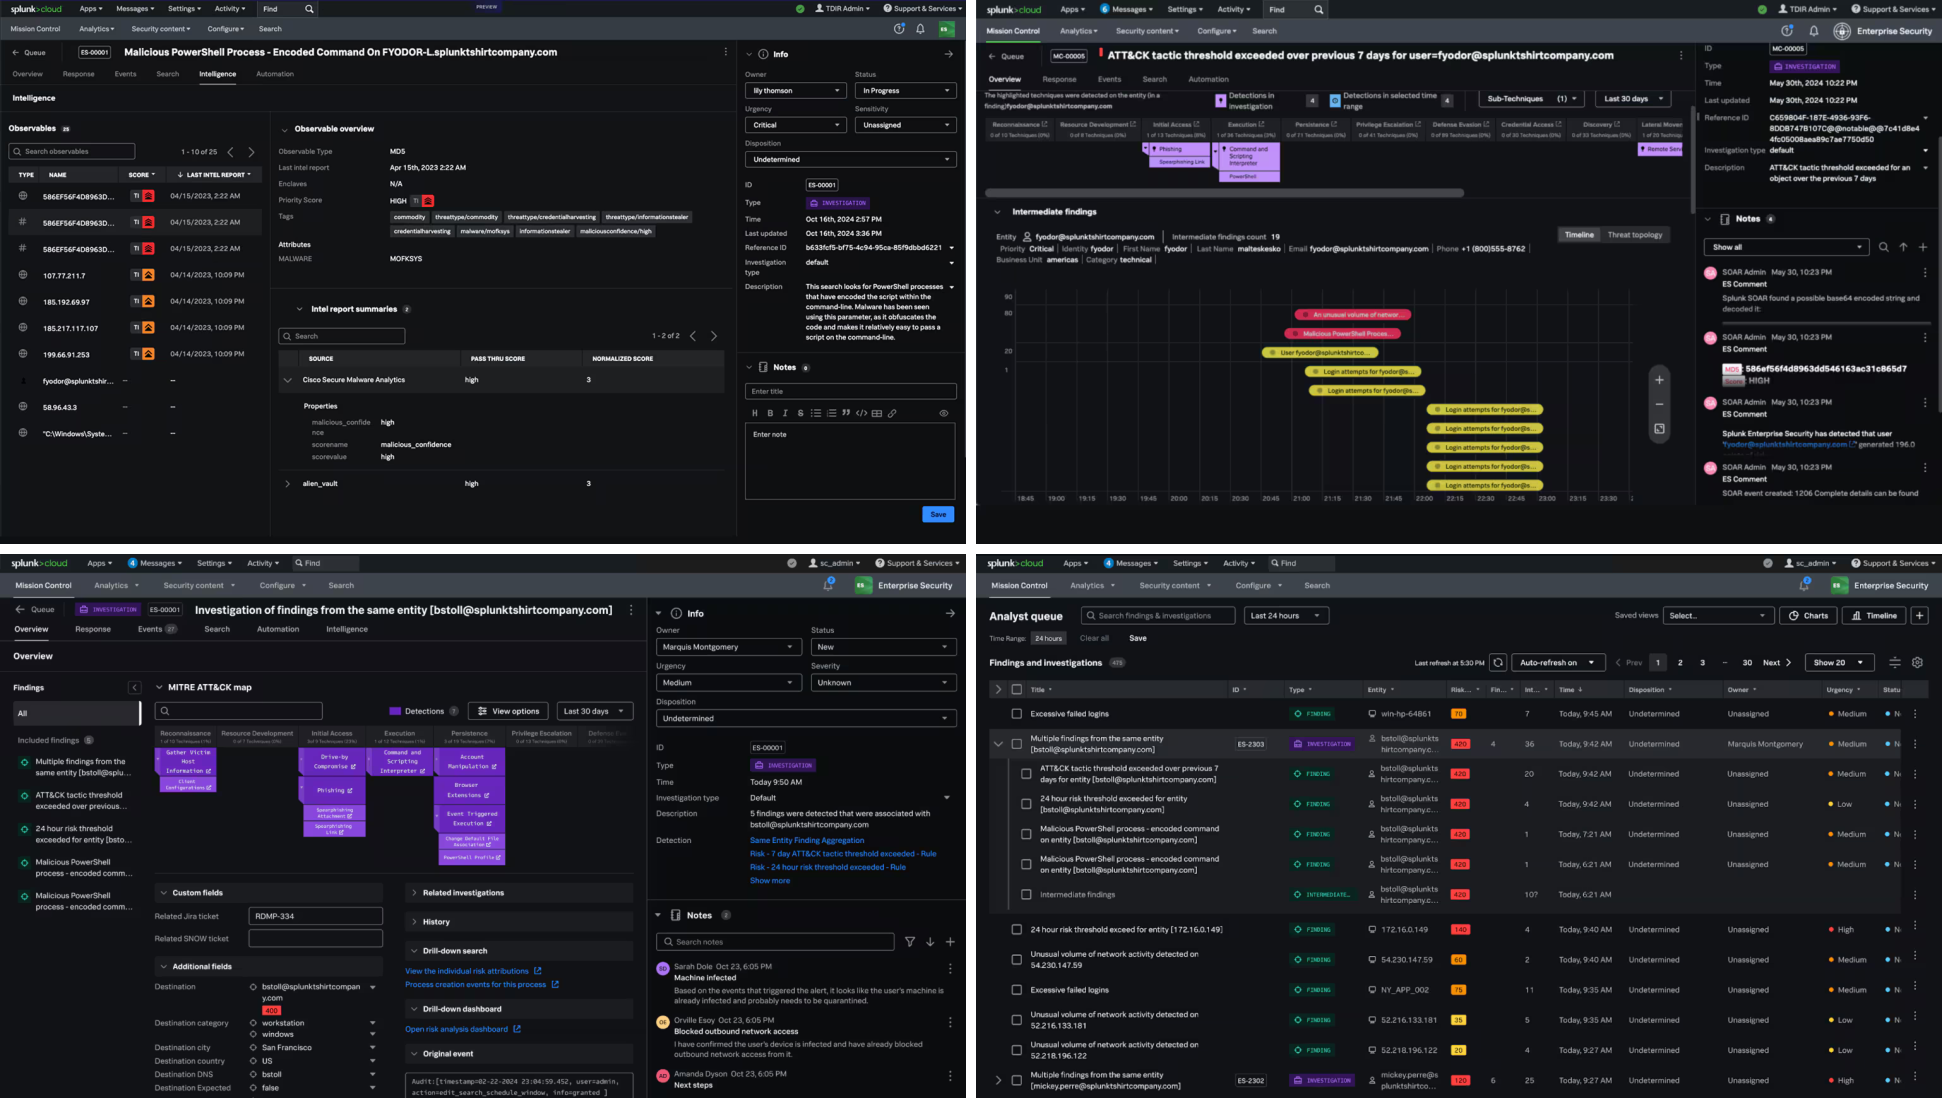
Splunk Enterprise Security is a SIEM-based SecOps platform that unifies threat detection, investigation, and response (TDIR) workflows into a single workspace. Built around SIEM, it combines SOAR, UEBA, threat intelligence, detection engineering, and asset visibility capabilities.
Where the previous section summarized the points IDC MarketScape assessed, this section looks at the underlying capabilities behind that assessment.
A Unified Workspace for Continuous Investigation
The analyst workspace is Mission Control. Because team-based work queues route findings according to configurable rule sets, different SOC teams can carry out their own work on the same instance. Shared case management groups correlated events into a single investigation view. Analysts move from reviewing findings to investigation and response within this same screen. Compared with a workflow where an analyst checks a detection in the SIEM screen, switches to a SOAR console to run automation, and then switches again to another screen to look up user behavior, the difference shows up not only in time spent on investigation but also in the consistency of the reasoning behind decisions.
How Detection Rules Are Built and Managed
Enterprise Security 8.x introduces detection version control with diff review and rollback. Detection Studio provides a single experience covering the writing, tuning, validation, and deployment of detection rules, and lets teams measure coverage against the MITRE ATT&CK framework to identify detection gaps. Given the detection tuning burden IDC flagged earlier, the ability to version-control detection rules and roll back to a previous version when problems arise is directly tied to operational stability.
Risk-Based Alerting and Threat Intelligence
Finding-Based Detections correlate individual risk events—using asset and identity context—into higher-confidence findings. Findings are built from observed details such as timestamps, key/value pairs, entity information, impact, risk score, and threat objects. Risk-Based Alerting (RBA) is layered on top of this, producing a normalized score from 0 to 100 based on findings associated with an entity. During incident review, analysts can expand the score to see the calculation history and a timeline of detection activity. Because prioritization is based on where risk is accumulating on a given entity rather than on raw alert volume, this is used to narrow down what needs to be worked. Threat intelligence provides normalized scoring together with context; Cisco Talos threat intelligence is available at no additional cost—an element that removes the need to check external intelligence in a separate tool during investigation.
Insider Threat Detection Through UEBA
UEBA uses behavior-based anomaly detection and machine learning to identify subtle deviations in user and entity behavior. Its primary targets are types of activity that are difficult to catch with signature-based detection, such as account misuse, credential theft, and lateral movement. The machine learning models and user behavior models can be tuned to an organization's processes, policies, assets, user roles, and operational functions. Because what counts as "normal" behavior differs by organization, whether the model can be calibrated to fit a given environment is a key factor in determining the false-positive rate.
SOAR-Based Response Automation
SOAR automates security workflows to reduce manual effort and response time. Splunkbase offers a SOAR app supporting more than 300 third-party tool integrations and more than 2,800 automation actions. Splunk describes this as a way to extend integration coverage without replacing an organization's existing security stack. This is paired with Response Plans, prompt-based automation, and a visual playbook editor—built so that even staff without extensive automation experience can standardize response procedures.
Asset and Risk Visibility
Asset and Risk Intelligence is in the process of evolving into Exposure Analytics. It discovers assets and identities from collected telemetry, enriches them with context, and applies pattern checks for configuration anomalies—an element that removes the need to look up asset context in a separate tool during investigation.
AI Agents for Individual SOC Tasks
Rather than a general-purpose assistant, Splunk offers six AI agents, each responsible for a specific SOC task. The Detection Builder Agent supports detection engineers as they move from hypothesis to production deployment; the SOP Agent converts standard operating procedures into response plans; the Triage Agent evaluates findings and explains the reasoning behind them; the Malware Threat Reversing Agent explains malicious script behavior and extracts indicators; and the Guided Response Agent and Automation Builder Agent turn approved procedures into executable response actions and SOAR playbooks. The work handled by all six agents is time-consuming and repetitive. Writing detection rules, triaging alerts, analyzing malware, and building playbooks are tasks that require skilled personnel but can be standardized—work the agents take on so that people can focus on judgment and approval.
☑️ What to Check When Evaluating a SIEM
IDC MarketScape also provides a checklist for technology buyers—one that can be used as a general SIEM evaluation checklist regardless of vendor.
- The level of integration with security tools and other tools already in use. When information is consolidated in one place, analyst screen-switching time drops and containment speeds up.
- The usefulness of vendor-provided content. Check the scope and update cadence of threat intelligence, detection rules, threat hunting content, and playbooks, and how well they align with frameworks such as MITRE ATT&CK.
- What can realistically be achieved with AI. Check the agent capabilities that operate within the workflow itself—alert triage, investigation, threat hunting, detection rule generation, and parser development.
- Time to actual detection coverage on major log sources, from initial deployment onward. Understand up front the time, personnel, and cost investment required.
- The investigation interface and case management capabilities. Check the flexibility of the query language and the extent to which context is provided without having to move between tools.
- Which deployment model is needed—on-premises, cloud, or hybrid. Regulatory and data sovereignty requirements can determine whether cloud operation is even possible.
- How compliance reporting works. Check whether data flows into a GRC solution as a structural pipeline, rather than relying on periodic manual export and import.
- Actual total cost of ownership. Examine where costs increase as data volume and retention periods grow.
- Whether the vendor offers a maturity-improvement program. Check whether the vendor benchmarks current detection, logging, and operational capability and provides an improvement roadmap.
☑️ Frequently Asked Questions
What is SIEM?
SIEM is a data platform that collects data from multiple sources, correlates alerts, initiates security investigations, and supports policy and compliance assurance. Its core role is identifying event patterns that may indicate an attack, intrusion, misuse, or failure. More recently, the scope of SIEM has expanded to include SOAR-style capabilities such as case management and automated workflows, as well as AI agents that operate under human oversight.
What is IDC MarketScape?
IDC MarketScape is an analytical model that assesses and positions the competitive fitness of technology and service vendors within a specific market. It applies both qualitative and quantitative scoring and places each vendor along two axes: current-state capability and alignment with strategy over the next three to five years. Vendor surveys and interviews, publicly available information, and actual customer experience all feed into the scoring.
What kind of product is Splunk Enterprise Security?
Splunk Enterprise Security is a SecOps platform that unifies threat detection, investigation, and response (TDIR) workflows into a single experience. Built on SIEM, it combines SOAR and UEBA and embeds role-specific AI into SOC workflows, allowing analysts to carry out investigation and response without switching between tools. It is offered in two editions: Essentials and Premier.
What is the difference between Splunk Enterprise Security Essentials and Premier?
The difference is in the scope of included capabilities. Essentials includes core SIEM, Threat Intelligence Management, Detection Engineering, and Exposure Analytics, plus AI Assistant. Premier adds Splunk SOAR, UEBA, and Threat Analysis on top of that. Organizations planning to apply automation and user behavior analytics from the outset should consider the Premier configuration.
Can it be used in an on-premises environment?
Yes. Splunk Enterprise Security can run as a self-managed deployment based on Splunk Enterprise, or as SaaS based on Splunk Cloud Platform on AWS, Azure, or Google Cloud Platform. Customers deploy it across on-premises, hybrid, and multi-cloud environments, collecting security and operational data on the same data plane. Note, however, that some AI capabilities are documented as cloud-delivered only in official materials, so the scope of features by deployment type should be confirmed.
☑️ Conclusion
In the 2026 IDC MarketScape SIEM assessment, Splunk Enterprise Security was recognized on four points: a unified working structure that completes investigations within a single screen; a base of community content that enables detections tailored to an organization's own environment; a data plane that handles security and operational data without duplication; and deployment flexibility that allows customers to choose where their data resides. All four points connect not to a feature list, but to operational burdens SOC teams actually face. Being named a Leader for the 11th consecutive time in the 2025 Gartner® Magic Quadrant™ for Security Information and Event Management is close to the cumulative result of this same kind of operational perspective in evaluation.
That said, being assessed as a Leader does not automatically mean the product is the right fit for a given environment. What remains is the process of designing the scope of data to be collected, integrating with existing security solutions, acquiring and tuning detection content, deciding on edition and deployment type, and embedding a workflow that operations staff will actually use.
CloudNetworks is an official Splunk partner that has carried out SIEM implementations across large-scale environments in finance, telecommunications, credit card, and e-commerce. Consolidating security data across affiliates, unifying monitoring across mixed on-premises and cloud environments, migrating existing detection rules, and SOAR automation are challenges CloudNetworks has actually worked through. If you are considering a SIEM transition or SOC operational improvement, please contact us through the 'Contact Us' button.
▶ Read the full IDC MarketScape 2026 SIEM report
▶ View Splunk products
[Source : IDC, "IDC MarketScape: Worldwide SIEM 2026 Vendor Assessment", IDC #US54126826e, June 2026, IDC, "IDC MarketScape: Worldwide SIEM 2022 Vendor Assessment", IDC #US49029922, November 2022, IDC, "IDC MarketScape: Worldwide SIEM for Enterprise 2024 Vendor Assessment", IDC #US51541324, September 2024, Gartner, "Magic Quadrant for Security Information and Event Management", 2025, Splunk, "Splunk Named a Leader in the 2026 IDC MarketScape for Worldwide SIEM", Splunk, "Splunk Enterprise Security", Splunk, "Enterprise Security Features"]