

Phishing is an old attack method. Yet it remains one of the areas where security operations teams spend the most time, and as attack techniques have grown more sophisticated recently, the difficulty of investigation has risen along with it.
The burden doesn't come from volume alone. The real work begins after a suspicious email is reported and an alert is generated. Message details have to be checked in one tool, link analysis in another, and artifact enrichment in yet another. All the while, analysts must also determine whether what they're looking at is the entire attack or just part of it. Multiply that by the number of alerts handled per day, and more time ends up being spent moving between tools than actually investigating.
Splunk Enterprise Security has added an Automated Threat Analysis capability aimed at this problem. It automatically executes and analyzes phishing attack chains, delivering the context and evidence needed for decision-making directly into the analyst's workspace. It brings core threat analysis capabilities that originated in Splunk Attack Analyzer directly into Enterprise Security, and is available in the Premier edition.
☑️ Why Phishing Investigations Drain SOC Time
Phishing attacks have moved beyond simply exposing a malicious link outright. There are three main ways attackers now increase investigation difficulty.
One is hiding the final destination behind a chain of redirects. Another is using QR codes to direct users outside the original email's path — this type often bypasses existing email gateways. A third is placing credential-harvesting pages behind a CAPTCHA gate, intended to make manual analysis harder and slow down the defender's response.
This is why a single email that initially looks simple can turn into an investigation requiring context to be pulled together from multiple tools.
On top of this, there are limitations in analysis tools. Legacy analysis tools often fail to provide analysts with sufficient signal to work from, forcing them to spend time on manual verification to answer questions such as:
- Is this message impersonating a known brand?
- Does the URL in question lead somewhere suspicious?
- Is there enough basis to escalate, or is this just noise?
Security teams handle a large volume of reported emails along with duplicates and false positives. If every suspicious email requires the same level of manual work, the SOC's time ends up being spent on things that aren't actually significant threats.
☑️ How Automated Threat Analysis Handles Phishing Investigations
Automated Threat Analysis is designed to bring high-accuracy phishing analysis directly into existing security workflows. Its operation breaks down into three parts: gaining visibility into phishing threats, conducting consistent investigations, and running end-to-end automated workflows.
Reported phishing emails visible directly in the Analyst Queue
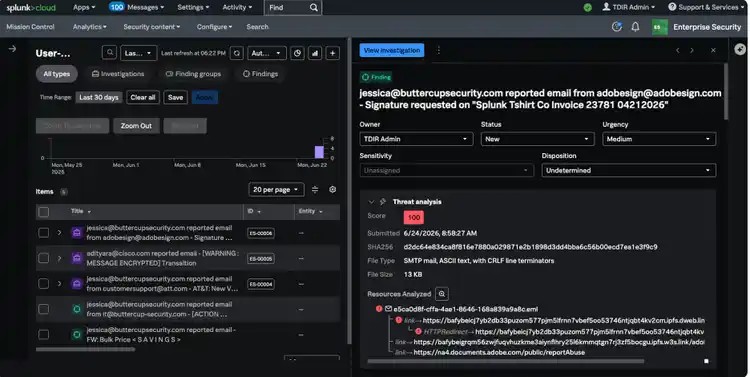
Automated Threat Analysis surfaces reported phishing emails directly in Enterprise Security's Analyst Queue and gathers the context needed for investigation in one place. Analysts can break down the phishing attack chain within the same environment where they already triage and categorize security events to determine whether they're real threats. Because the attack chain is automatically broken down within Enterprise Security, the scope and severity of a threat can be understood with less manual effort.
This approach preserves the security context surrounding the email, since affected users, related systems, other activity linked to the same entities, and any ongoing investigations can all be reviewed together. As a result, tool-switching is reduced for experienced analysts, a workflow that's easier for less experienced analysts to follow and trust is created, and phishing investigation speed improves across the entire SOC.
Investigation evidence with automatically extracted verdicts and impersonated brands
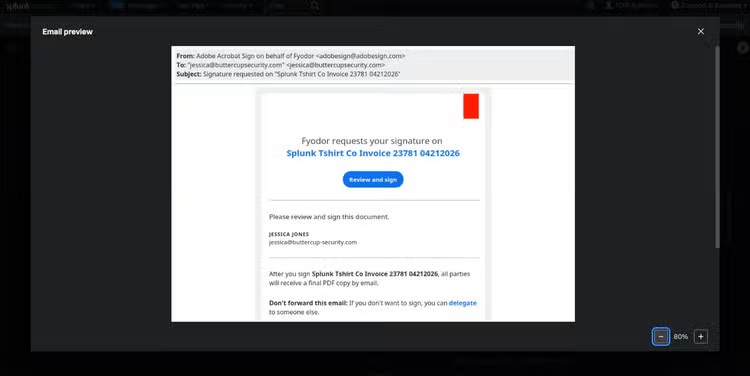
Having context available within the workflow isn't enough on its own — it needs to be usable for actual decision-making. To answer the questions above inline, Automated Threat Analysis provides evidence such as Verdict and Confidence, system tags, phishing kit family, impersonated brand, and automatically extracted content — email screenshots, embedded URLs, QR codes, and a resource chain showing how URLs and QR codes trace to their final destination.
Email screenshot capture is another quick way to verify impersonation and visual deception. Brand-impersonation types that are hard to judge from text-based indicators alone can be checked directly within Enterprise Security.
By automatically extracting and surfacing this evidence, analysts can quickly grasp what they're looking at, why it's suspicious, and what the attacker is after. Because threat context is delivered within the analyst's primary workspace, investigations are simplified and response time can be shortened based on trustworthy results. Triage speed, escalation decisions, and overall confidence in SOC judgments all improve together.
Risk-score-based prioritization linked to response automation
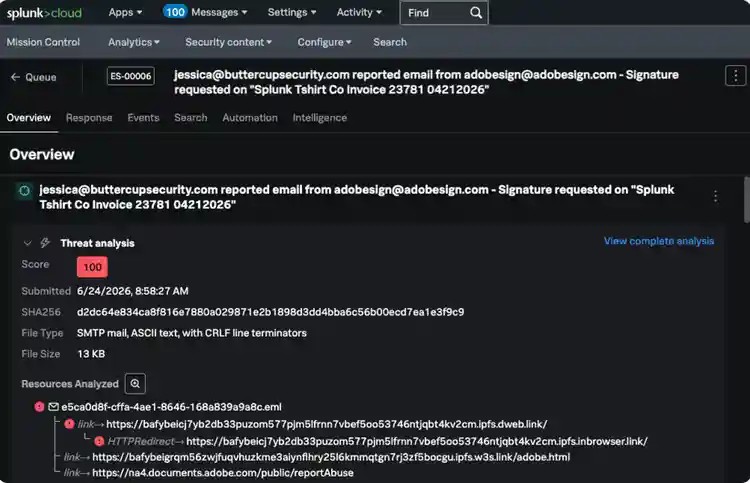
Automated Threat Analysis provides a risk score from 0 to 100, with higher scores indicating higher risk. Emails with high scores are treated as priority items likely to represent real threats.
This capability filters out low-risk items early and surfaces strong signals first, reducing unnecessary investigative work. It's not just that individual investigations get faster — it changes how the SOC allocates time across the entire queue.
Prioritized analysis results then feed into the response stage. Using Automated Threat Analysis together with Enterprise Security's native SOAR and AI capabilities makes it possible to build intelligent automation and operate end-to-end workflows.
☑️ Key Features of Automated Threat Analysis
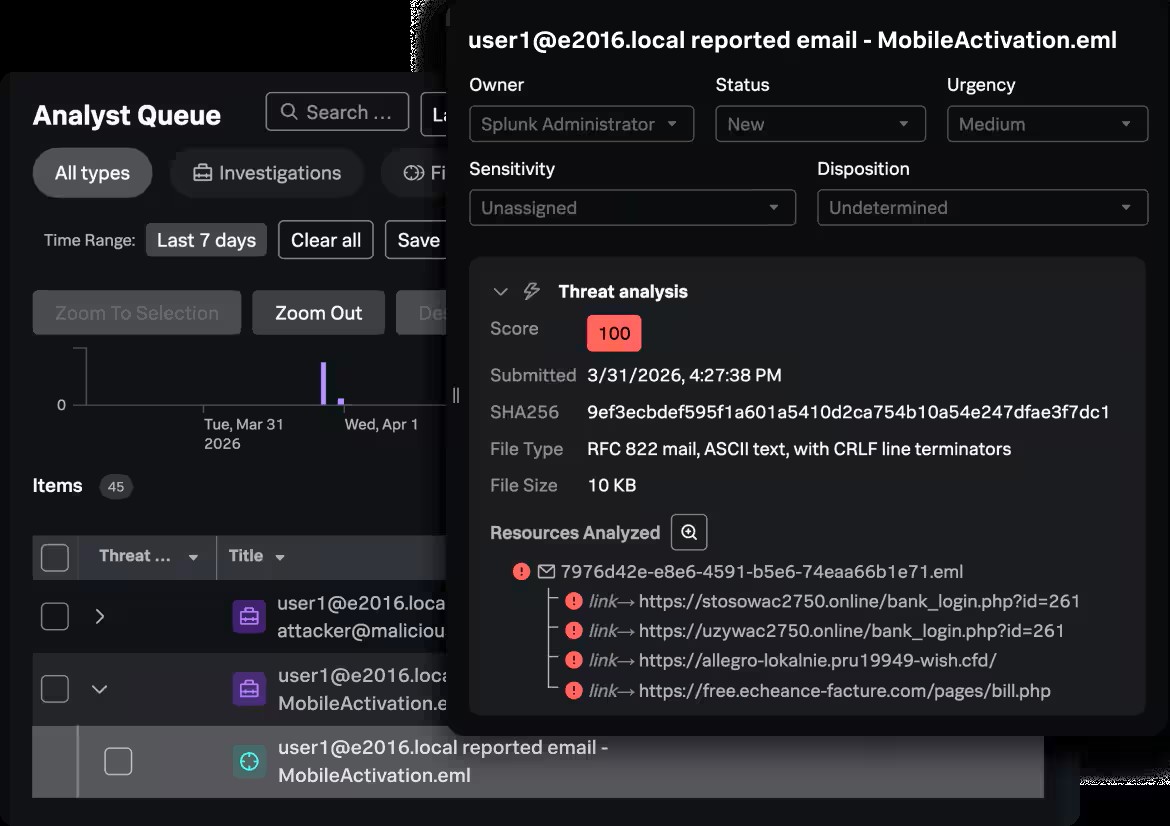
The investigation flow described above runs on top of the analysis capabilities that Automated Threat Analysis provides by default. Automated Threat Analysis breaks down phishing attack chains and delivers automated phishing forensics results directly into the analyst's primary workspace. Its role is to eliminate tool-switching and manual investigation work so the SOC can investigate, respond to, and neutralize phishing threats faster, more accurately, and with trustworthy results.
Its features can be summarized in three points:
- Automated attack chain analysis: Automatically analyzes the attack chain through to the final payload. Even in structures with multiple intermediate steps such as redirects or QR codes, this reduces manual work while providing comprehensive visibility into malicious activity.
- Actionable threat summary: Provides an overview of analysis results, including threat scores and analyzed resources, so severity and attacker intent can be assessed before reviewing individual indicators one by one.
- Detailed threat forensics: Extracts malicious content during analysis and records triggered detections in detail — information that can be used for deeper investigation of incidents after initial triage.
☑️ Splunk Enterprise Security Components and Editions
Splunk Enterprise Security is a unified threat detection, investigation, and response (TDIR) platform that integrates agentic AI, SOAR, UEBA, and SIEM. It's because Automated Threat Analysis runs on this platform that investigations can continue without switching tools.
Key components provided by Enterprise Security include:
- SIEM: Manages, searches, and analyzes data across domains, cloud, and devices. AI-driven detection and alert prioritization help SOC teams focus on true positives.
- Risk-Based Alerting (RBA): Reduces alert volume by up to 90% through high-accuracy threat detection, raising the true-positive rate so teams can focus on significant threats.
- SOAR: Automates security workflows to reduce manual work, alert fatigue, and response time.
- UEBA: Uses machine learning and behavior-based anomaly detection to identify insider threats and advanced threats early, such as account misuse, credential theft, and lateral movement.
- Detection Studio: Provides a lifecycle covering detection planning, development, testing, deployment, and monitoring, and measures coverage against the MITRE ATT&CK framework. Available in AWS cloud environments.
- Exposure Analytics: Continuously identifies assets and users and adds detailed context to security events to support risk prioritization.
- Threat Intelligence: Cisco Talos threat intelligence is available at no additional cost.
- AI Assistant: Provides natural language queries, guided workflows, summaries, and automated reporting.
- Federated Search and Federated Analytics: Support search and analytics regardless of where data resides.
Enterprise Security is offered in two editions, Essentials and Premier, and Automated Threat Analysis is included in the Premier edition.
| Feature | Essentials Edition | Premier Edition |
| SIEM | Included | Included |
| Threat Intelligence | Included | Included |
| Detection Studio | Included | Included |
| Exposure Analytics | Included | Included |
| SOAR | Not included | Included |
| UEBA | Not included | Included |
| Automated Threat Analysis | Not included | Included |
☑️ The Relationship Between Splunk Attack Analyzer and Automated Threat Analysis
Splunk Attack Analyzer is a standalone solution specialized in malware and phishing analysis. Automated Threat Analysis is a native capability built directly into the Premier edition, bringing in many of the core threat analysis capabilities that originated in Splunk Attack Analyzer. Further feature enhancements are planned in upcoming releases.
☑️ Frequently Asked Questions
What is Automated Threat Analysis?
Automated Threat Analysis is a built-in capability of Splunk Enterprise Security Premier edition that automatically analyzes phishing attack chains and delivers forensic insights and threat context directly into the analyst's primary workspace. Analysts can triage and investigate phishing threats without leaving Enterprise Security.
Can it also analyze QR code phishing (quishing)?
Yes. Automated Threat Analysis uses OCR and image analysis to automatically decode QR codes and trace embedded URLs to their final destination. Quishing attempts, which often bypass existing email gateways, can be analyzed and triaged within the Enterprise Security environment.
Which edition is it available in?
Automated Threat Analysis is available in the Splunk Enterprise Security Premier edition. It's not included in the Essentials edition; SOAR and UEBA are also Premier edition features.
How is it different from Splunk Attack Analyzer?
Splunk Attack Analyzer is a standalone solution specialized in malware and phishing analysis, while Automated Threat Analysis is a native capability built into the Premier edition. It brings core threat analysis capabilities that originated in Splunk Attack Analyzer into Enterprise Security, with further feature enhancements planned.
How does it help reduce phishing mean time to respond (MTTR)?
It contributes by reducing the manual work previously done by switching between multiple tools. Because high-accuracy phishing analysis takes place within the same workspace where the SOC already runs its detection, investigation, and response workflows, the time from triage to response can be shortened.
☑️ Closing
As phishing attacks have shifted toward using redirect chains, QR codes, and CAPTCHA gates, the way they're investigated needs to change as well. Automated Threat Analysis handles phishing attack chain analysis within Splunk Enterprise Security to reduce tool-switching, delivers evidence such as verdicts, impersonated brands, and resource chains directly to analysts, and supports prioritizing work by risk score while connecting through to response automation.
CloudNetworks supports customers from adoption review through to operation, drawing on a dedicated Splunk team and accumulated implementation experience. If you need a solution tailored to your environment — including reviewing Enterprise Security edition configuration, designing phishing response processes, or SOAR integration — please reach out via the link below.
▶ View Splunk Products
[Source: Splunk, "Automated Threat Analysis: Centralize and Accelerate Phishing Investigations in Splunk Enterprise Security," https://www.splunk.com/en_us/blog/security/centralize-and-accelerate-phishing-investigations-in-splunk-enterprise-security.html; Splunk, "Automated Threat Analysis," https://www.splunk.com/en_us/products/automated-threat-analysis.html; Splunk, "Splunk Enterprise Security," https://www.splunk.com/en_us/products/enterprise-security.html]