

AIM Intelligence
AI Red Teaming & Guardrail Platform
AI Red Teaming & Guardrail Platform
AI agents are making decisions, calling APIs, and taking actions — with no one watching. AIM Intelligence attacks your AI before real attackers do, and enforces real-time guardrails to keep every agent under your control.
Tackle your most pressing AI challenges. From red teaming and real-time guardrails to security framework consulting. Resolve complex AI risks at once with AIM Intelligence’s integrated solutions.
The AI red teaming platform that attacks across every modality — text, image, audio, video, and physical AI. From foundation models to autonomous agents and production applications, Stinger finds critical vulnerabilities before attackers do.
개인정보, 영업비밀 등 민감한 데이터를 탐지하고 보호합니다. 성능 저하를 최소화하면서 초저지연 가드레일과 자율 에이전트를 통해 비정상적인 API 호출을 제어합니다. 퍼플팀 구성 및 직관적인 운영 기능을 갖춘 풀스택 보안 플랫폼입니다.
Evolving AI cannot be contained by simple keyword blocking or text moderation tools. AIM Intelligence delivers complete control over AI through multi-modal defense, customizable enterprise policies, self-improving guardrails, and agent security.
We don't wait for incidents. Our research teams identify next-generation threats at top AI conferences — before they appear in the wild. Published at ICLR, ICML, and ACL, Multi-modal and agentic threat research, Proprietary attack taxonomy.
We think like attackers. By proactively stress-testing your AI with millions of scenarios, we expose vulnerabilities that traditional testing misses. Millions of automated attack scenarios, Beyond prompt-level — end-to-end agentic red teaming, Text, image, audio, video, and physical AI.
Static rules break. Our guardrails continuously learn and adapt to your enterprise environment — blocking threats in real time without slowing down your AI. Self-improving, policy-aware guardrails, Ultra-low latency, zero disruption, Enterprise-grade operations with purple teaming.
Beyond simple text-based LLMs, spanning image, audio, video, and robotics-based Physical AI. AIM Intelligence securely controls all input and output modalities where AI interacts.
Seamlessly integrates into your existing infrastructure — regardless of model, deployment, or scale. Red teaming and guardrails in a single platform. One integration, complete lifecycle coverage from development to production. From proprietary LLMs and custom-built agents to commercial APIs like ChatGPT and Gemini — even coding agents like Claude Code and GitHub Copilot. One platform that secures them all. Deploy as cloud SaaS or fully isolated on-premise — tailored to your data governance and compliance requirements.
The AI red teaming platform that attacks across every modality — text, image, audio, video, and physical AI. From foundation models to autonomous agents and production applications, Stinger finds critical vulnerabilities before attackers do.
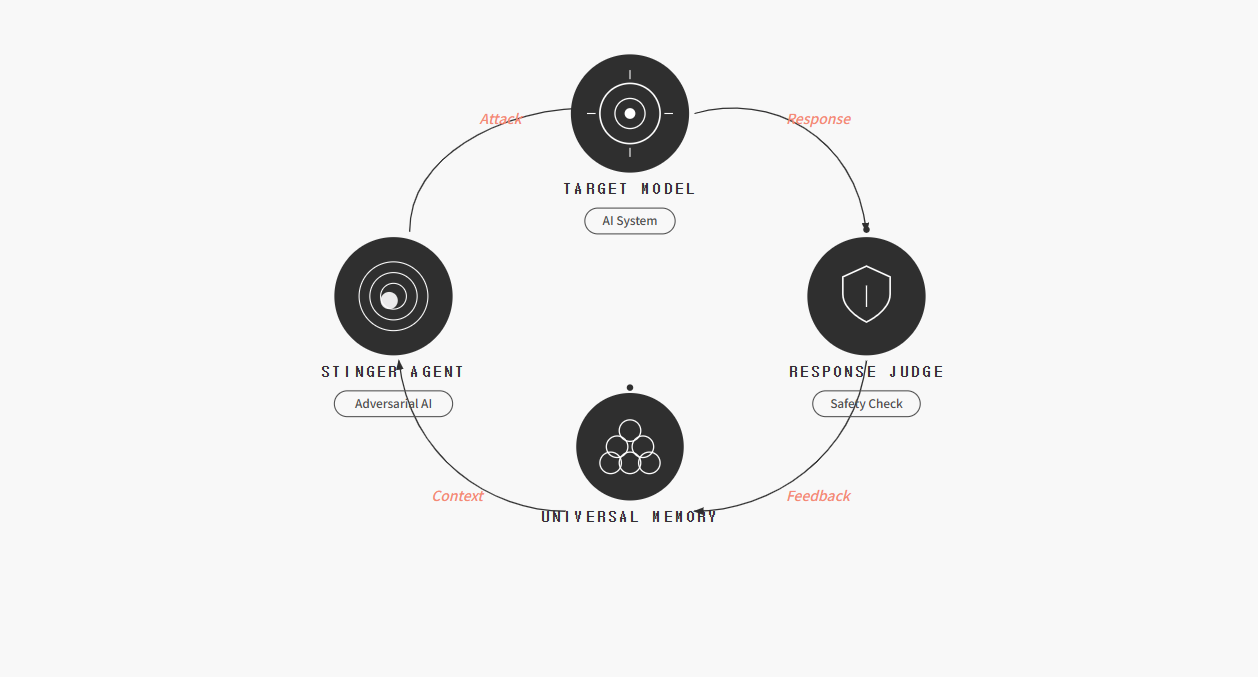
From mass single-prompt assaults to context-aware multi-turn jailbreaks that build trust before striking.
· 20,000+ attack tactics per mode
· Average 3.5 turns to exploit
· Crescendo, Tree-Search, ActorAttack
Attacks targeting RAG pipelines — injecting malicious payloads through documents your AI trusts.
· 21 payload types across 6 file formats
· 14 stealth injection techniques
· 4 risk categories with full coverage
Specialized attack vectors for every modality your AI processes — not just text.
· Text: prompt injection, role hijacking, encoding attacks
· Image: adversarial perturbation, harmful content
· Audio & Video: noise injection, safety eval
Attack your live applications directly — chatbots, agents, AICCs — and benchmark against foundation models side by side.
· Auto-crawl and target analysis
· Session Manager for auth state
· Custom Attack Goals per endpoint
Define your own evaluation criteria, and get executive-ready reports with vulnerability matrices and remediation guidance — automatically.
· Custom LLM-based judge
· Attack Technique x Vulnerability Matrix
· Comparative benchmarks & recommendations
IP protection, supply chain data leakage, and proprietary process extraction scenarios.
Regulatory compliance, hallucinated financial advice, unauthorized transaction scenarios.
Classified information extraction, adversarial manipulation, and operational security testing.
Real-time guardrails that protect every AI interaction — from sensitive data leaks and malicious prompts to abnormal agent behaviors. Ultra-low latency, zero disruption, full control.
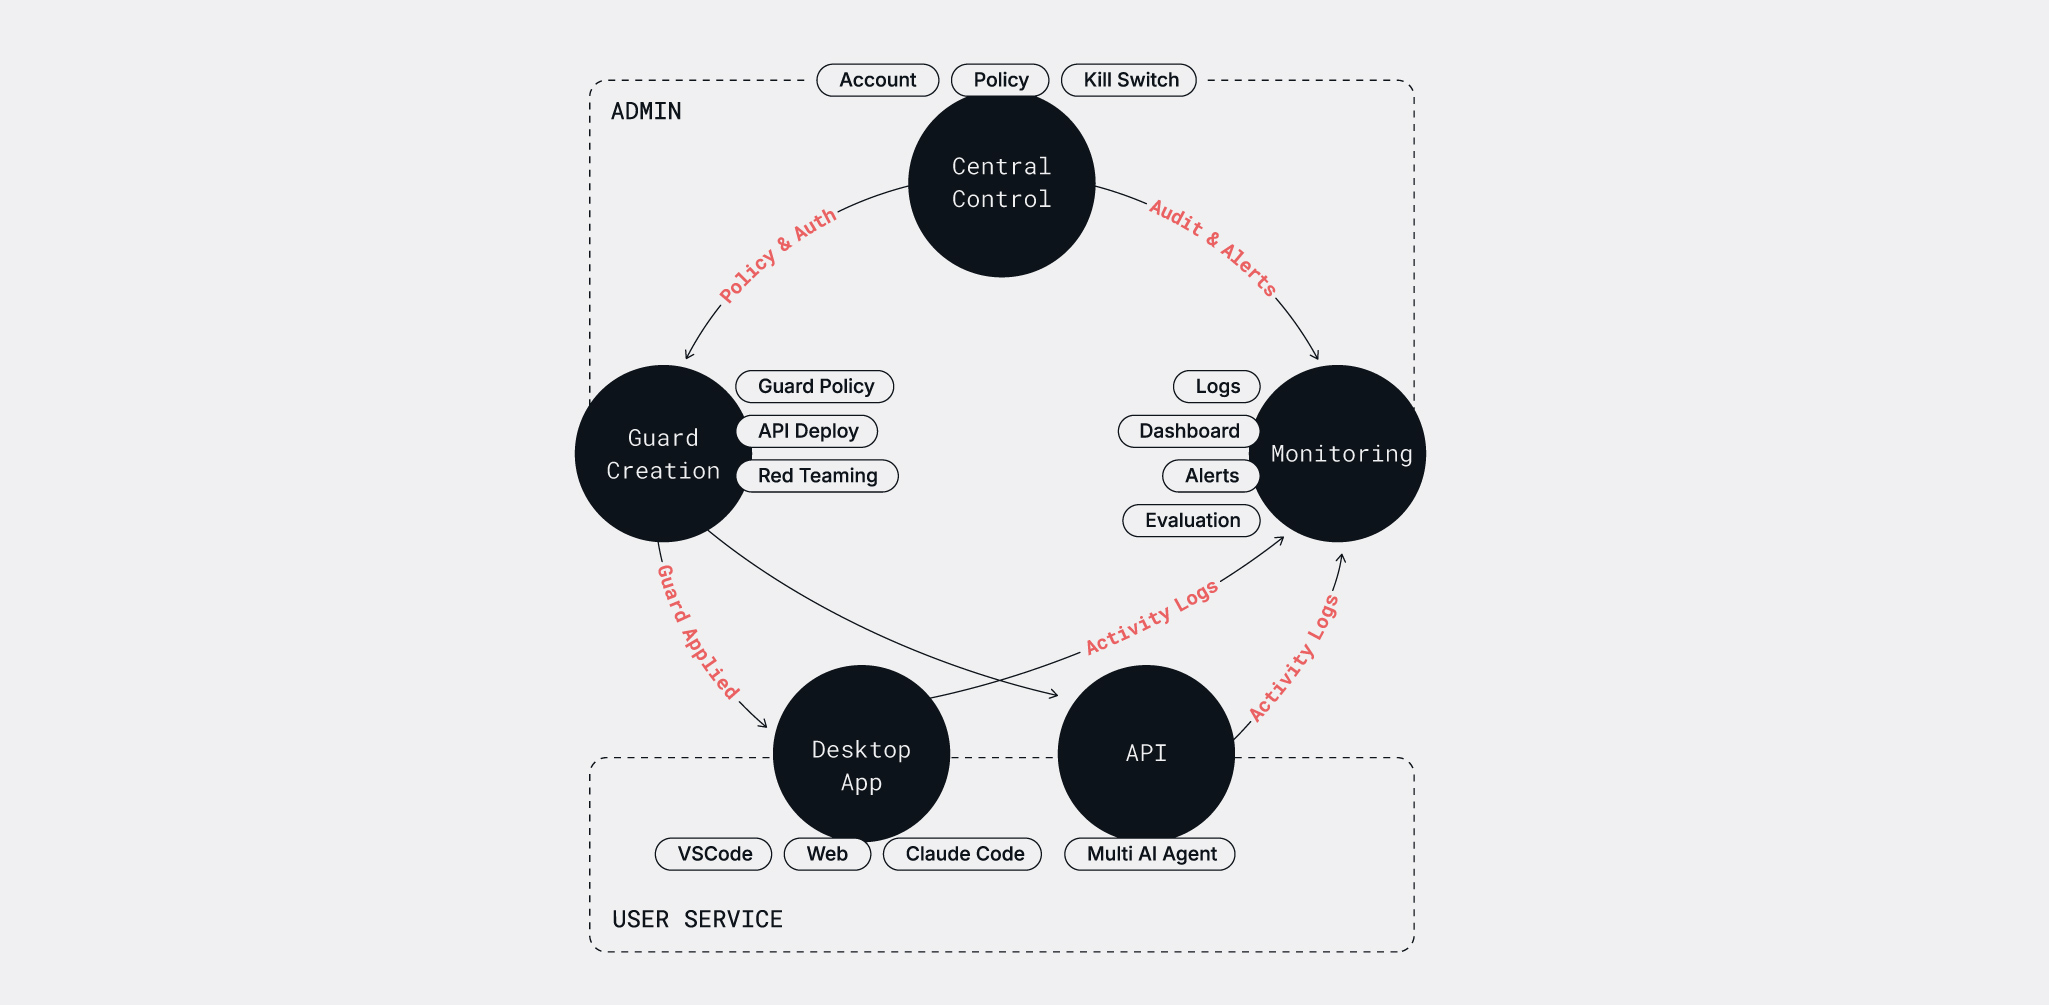
Purpose-built lightweight model that delivers industry-leading detection accuracy at ultra-low latency — protecting not just prompts and responses, but tool calls, function arguments, and agent decisions.
· Proprietary SLM + VLM architecture
· Best-in-class TPR with minimal false positives
· Intercepts tool calls, API invocations, and agent actions in real time
Far beyond regex. A multi-layered detection system that catches what others miss — PII, trade secrets, credentials, and more across every file type.
· 4-layer detection: Regex → NER → Context → Keyword
· Multi-modal file masking (PDF, DOCX, images, etc.)
· Proven to outperform leading guardrail solutions
Define security, compliance, and service quality policies with natural language examples — then enforce them across your entire organization. Auto-Forge keeps policies current by automatically updating rules based on emerging threats.
· AI Security · Regulatory · Service Quality policies
· Auto-Forge: automatic policy updates from new threat intelligence
· RBAC & multi-tenancy with policy inheritance
Full visibility into every AI interaction. Track policy violations, inspect blocked requests, and trace issues — with built-in purple teaming that feeds Stinger's attack findings directly into your defense posture.
· Opticon dashboard for centralized oversight
· Purple teaming: red team findings → guardrail updates
· Request-level logging and audit trails
Protect AI at every layer — from infrastructure proxies and API services to individual employee endpoints.
· Proxy layer: LiteLLM, Kong AI Gateway integration
· API/SDK layer: direct service integration
· Desktop Agent: endpoint control for ChatGPT, Claude, Gemini, Cursor, Copilot
Connect directly to your AI service via API or SDK. Ideal for customer-facing applications where every request needs real-time protection.
Deploy as a server proxy within your infrastructure. Supports AWS Bedrock, Azure AI, Vertex AI, and local models via LiteLLM or Kong AI Gateway.
Endpoint control for Windows & Mac. Auto-detects AI tool usage and inspects & masks sensitive data before it leaves the device.
Best for
Organizations with GPU resources and sensitive data requirements
Deploy
Your datacenter or private cloud
Pricing
Annual license
Best for
Fast adoption with operational convenience
Deploy
AIM-managed cloud
Pricing
Usage-based