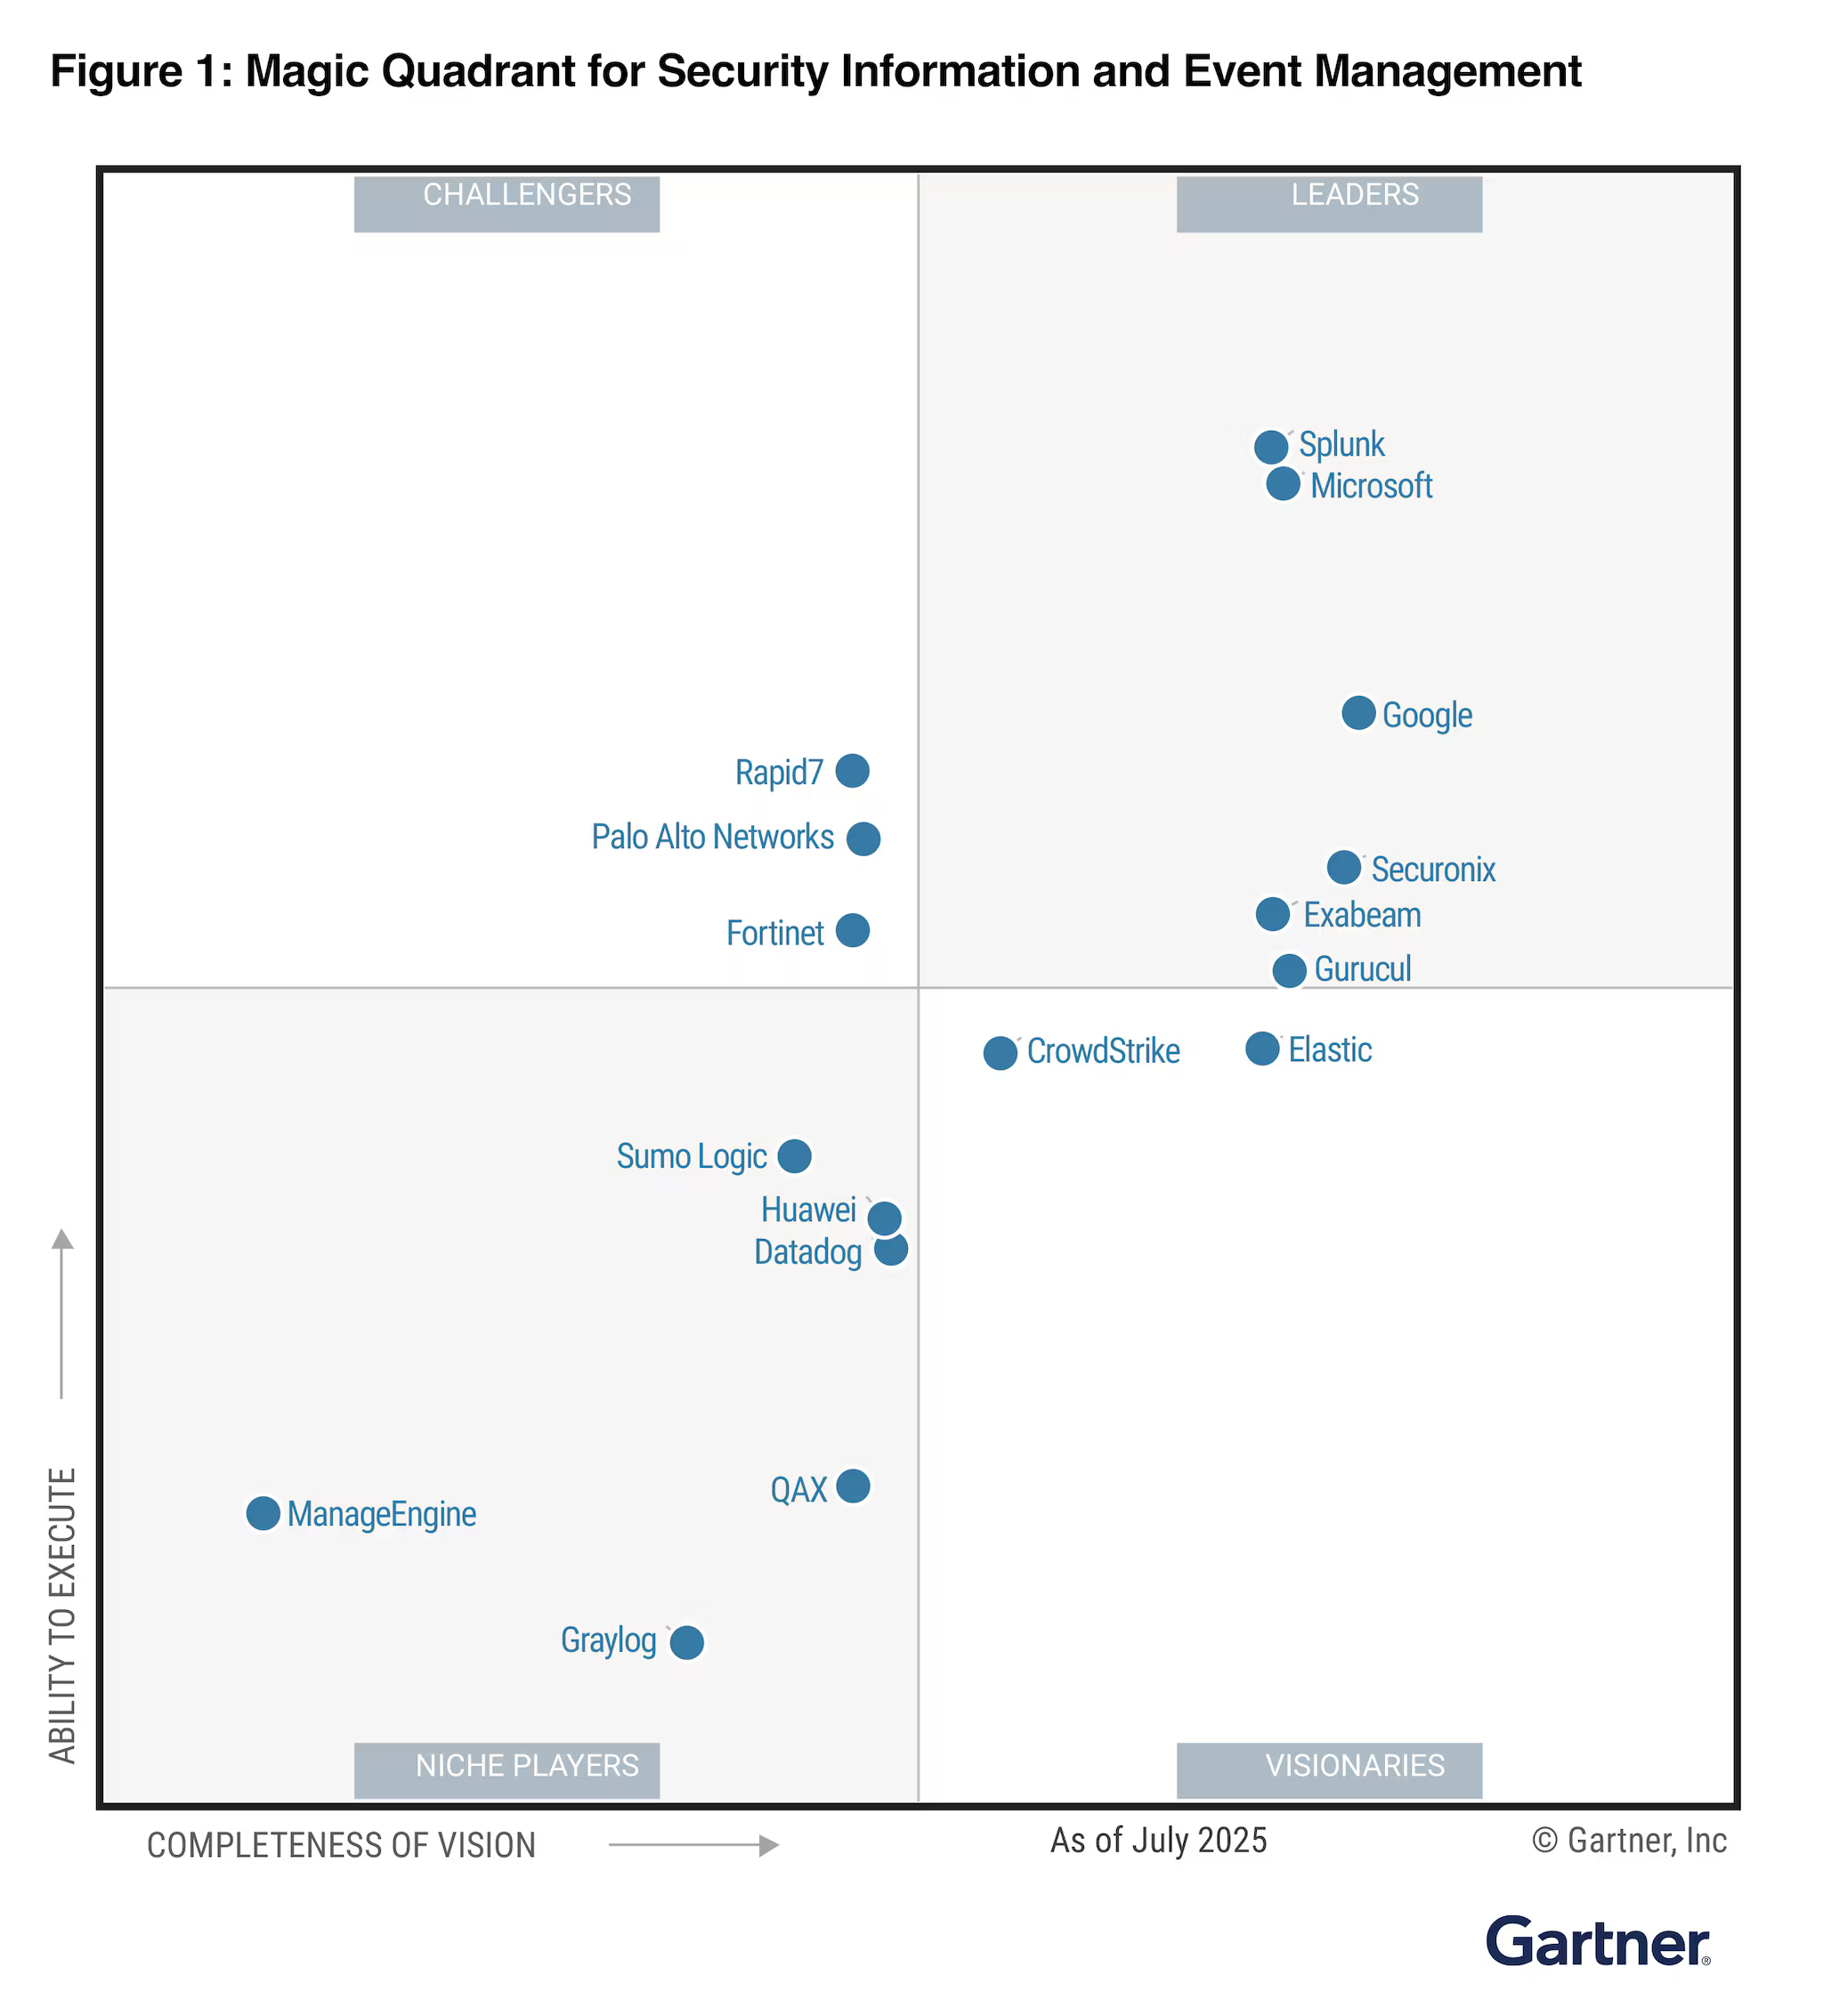
Splunk has been recognized as a Leader in the 2025 Gartner Magic Quadrant for SIEM (Security Information and Event Management) for the 11th consecutive year. Splunk stated that it was positioned highest for Ability to Execute.
This reflects Splunk's product strategy and customer outcomes in helping security teams respond proactively in a rapidly changing threat landscape.
✅Our Journey Together: Redefining the Next Era of the SOC
In the mid-2010s, Splunk launched Splunk Enterprise Security with a bold vision: to deliver a SIEM that could take in any data, at any scale, and make it immediately useful for security. This vision soon became reality and redefined how SOCs detect, investigate, and respond to threats (TDIR).
From a flexible SIEM that did not require a predefined schema to today's AI-enhanced SecOps platform, this journey has been shaped through collaboration with customers. Real-world challenges such as exploding data volumes, increasingly sophisticated threats, analyst shortages, and alert fatigue have been turning points at every stage. Customer feedback, trust, and partnership have accelerated Splunk's evolution. We have built a movement that goes beyond products, and we are leading security operations into the era of agentic AI.
✅A Unified AI-Powered SecOps Platform
At .conf25, Splunk unveiled the next chapter of Splunk ES (Enterprise Security). As a unified AI-powered SecOps platform, it simplifies the analyst experience and delivers faster, smarter outcomes across the entire threat detection, investigation, and response (TDIR) workflow. Here are some recently introduced innovations based on customer feedback.
Simplifying the Analyst Experience with Unified Workflows
Built-in SOAR for every analyst: Case management, playbooks, and automation are now built into ES, so every analyst can benefit from the speed and efficiency of automation.
Expanding Detection and Visibility
Accelerating the SOC with AI and Agentics
Splunk delivers AI that works the way the SOC works. In other words, purpose-built AI embedded across the entire analyst workflow, grounded in operational reality and measurable outcomes. Highlights include:
✅Conclusion
As we move into the era of agentic AI, Splunk's focus remains unchanged: ending analyst fatigue in the SOC, delivering faster outcomes, lowering risk, and building stronger resilience together. The unified AI-powered SecOps and expanded detection and automation capabilities of Splunk Enterprise Security turn this goal into an actionable reality. Download the report below to learn more about why Splunk was recognized.
▶ Download the 2025 Gartner Magic Quadrant for SIEM Report
▶ Learn More About Splunk Enterprise Security
Splunk Enterprise Security is a unified threat detection, investigation, and response (TDIR) platform that streamlines security workflows into a unified environment. It integrates capabilities including security information and event management (SIEM), agentic AI and SOAR for automation, and user and entity behavior analytics (UEBA) and AI/ML for improved detection accuracy and response speed. By bringing these capabilities together in a single interface, Enterprise Security reduces inefficiencies, eliminates tool silos, and ensures SOC teams can detect, investigate, and respond to threats more effectively.
Drawing on its expertise in big data, CloudNetworks operates a dedicated team specializing in the implementation and technical support of the Splunk platform. For inquiries about adopting and using Splunk, please contact CloudNetworks, an official partner.